Human proof for AI agent actions
Before an agent acts, demand proof of an attentive human.
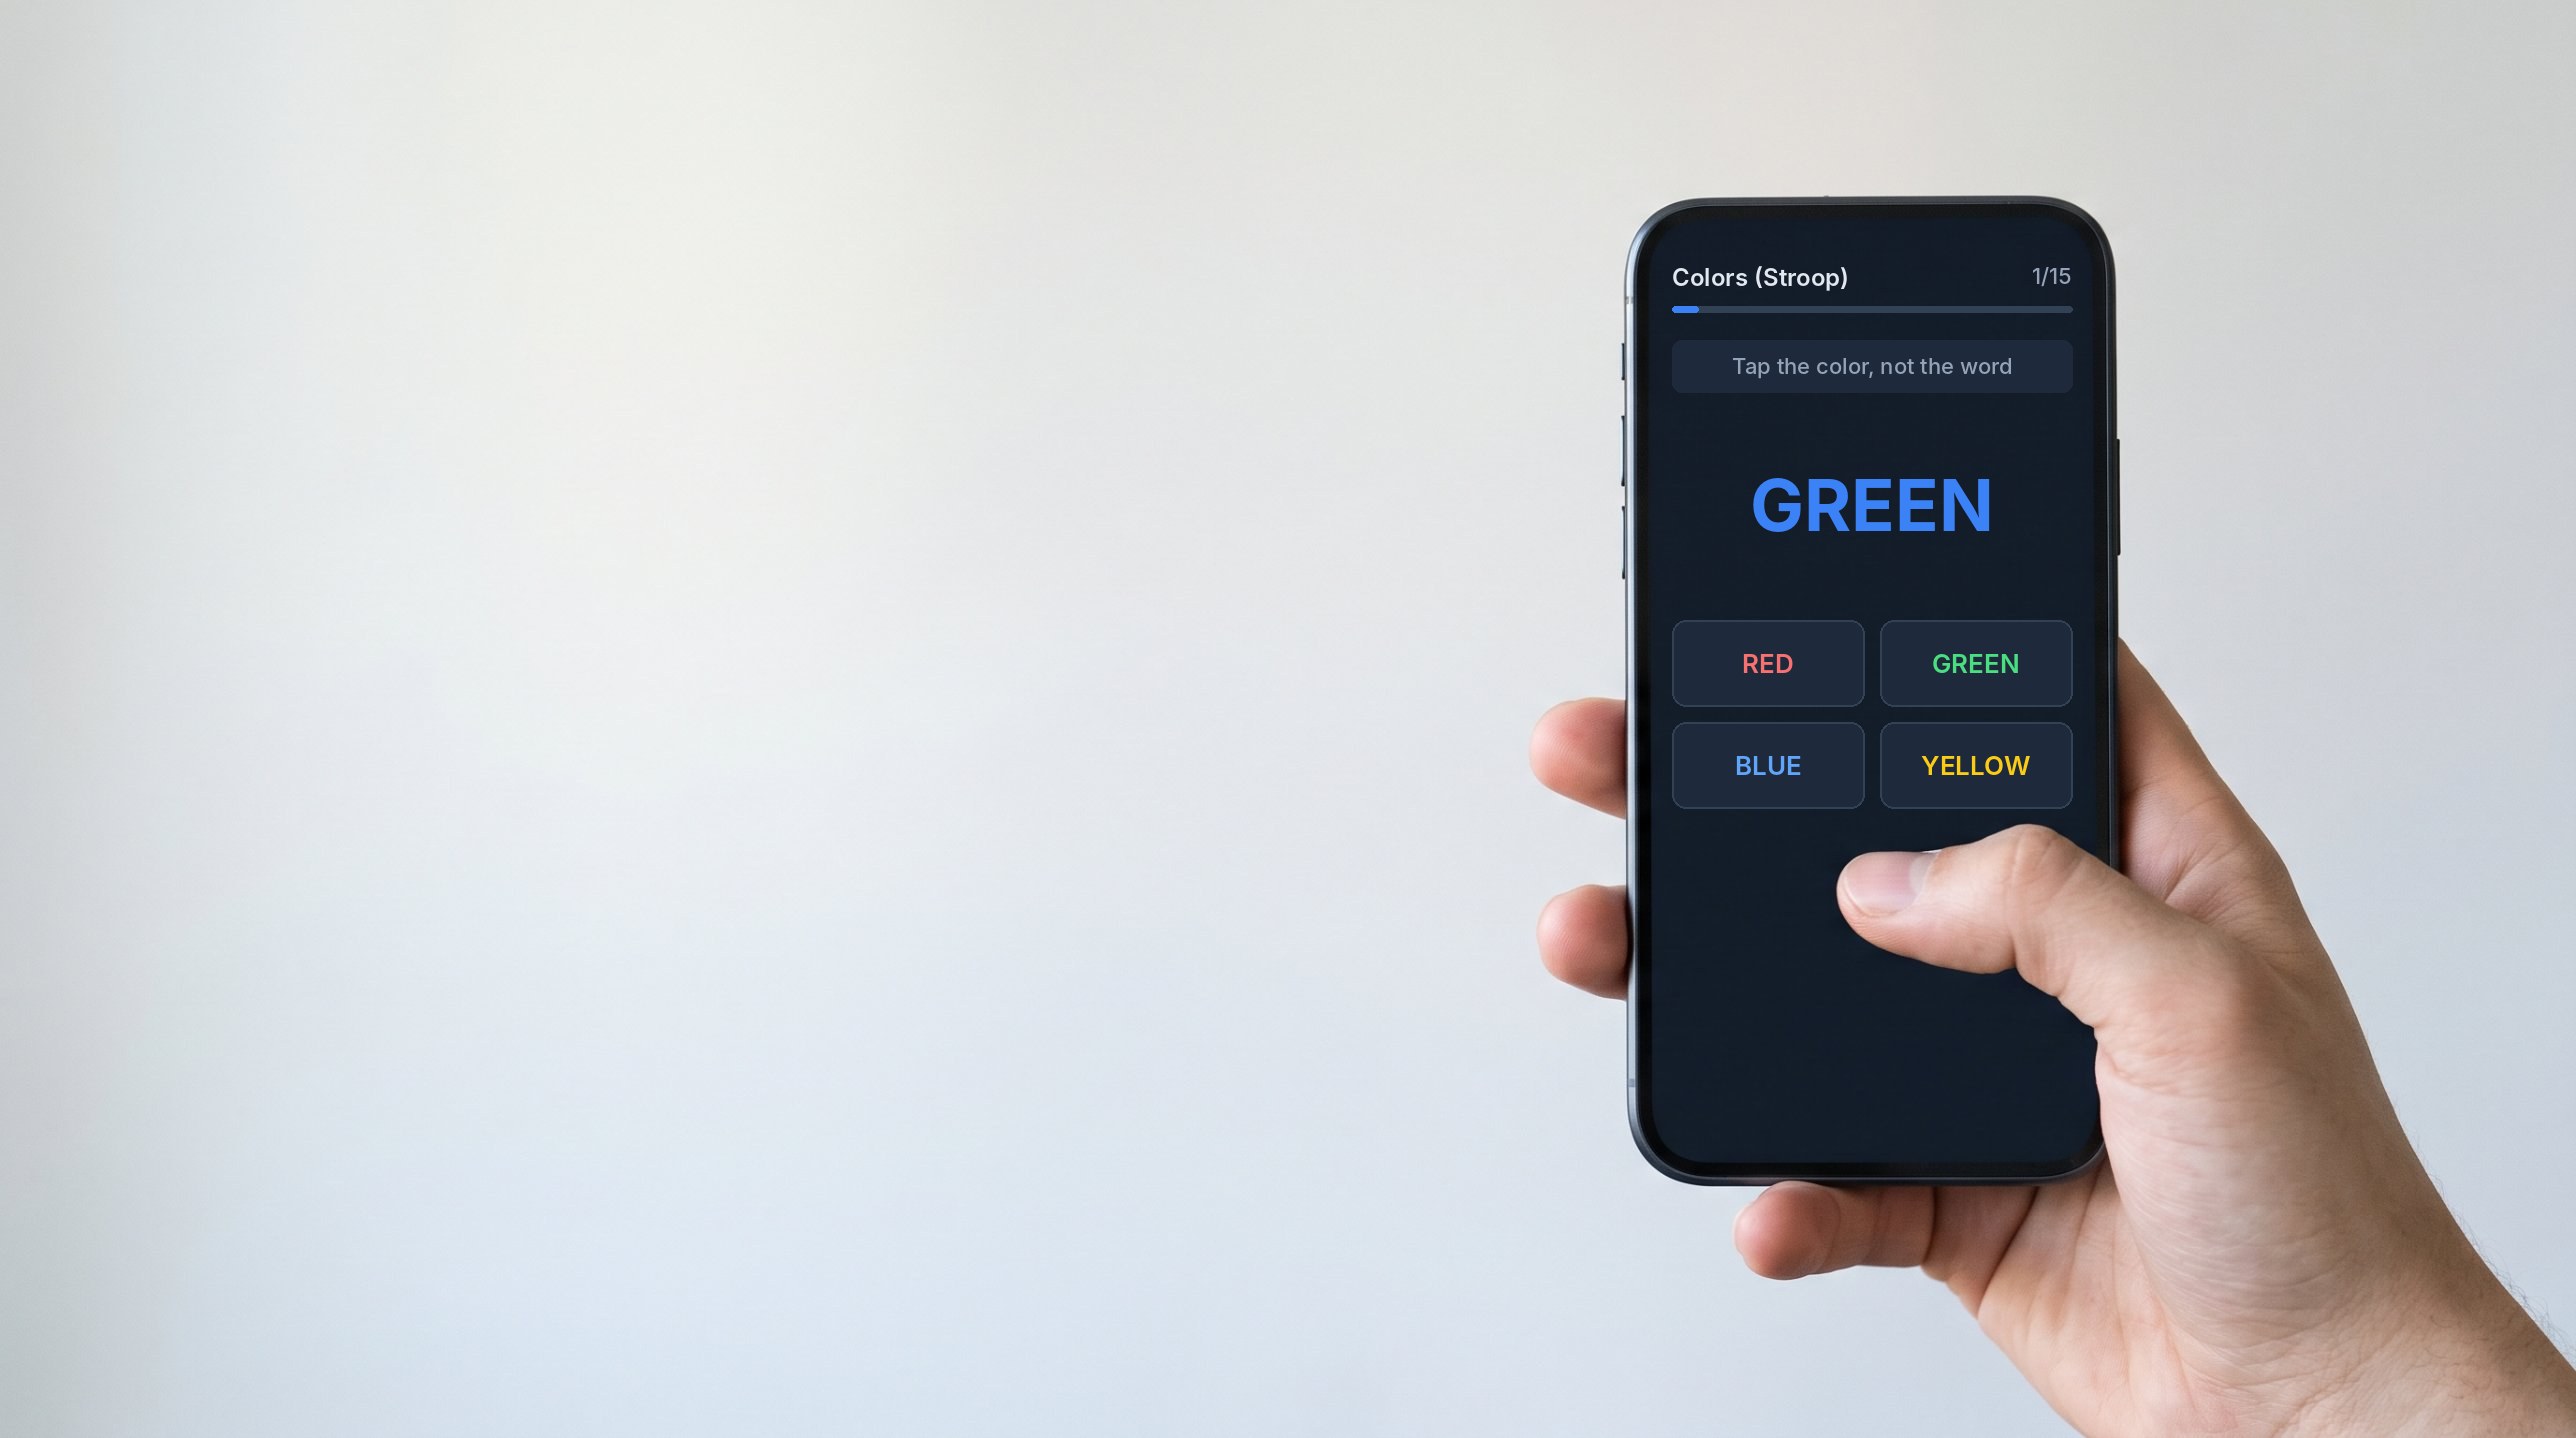
A standard approval only proves that a button was clicked. GateGuard verifies the person with a passkey, runs a short cognitive check on their phone, and seals the result in a proof signed twice, once with a post-quantum algorithm.
PROOF ggp_01M77V6H36NK
Approved, 12:19:54 UTC
A click on Approve proves very little.
Agents now act on their own, and the usual safeguard is a person pressing a button. A click does not show who pressed it, what they read, or whether they were paying attention. GateGuard records all three.
WHO
The right person
A passkey on their own phone, unlocked with a fingerprint, a face or the device code. No password, nothing to phish.
WHAT
The exact action
The sentence the person read is sealed into the proof. Change one character afterwards and the proof no longer verifies.
PRESENT
Actually paying attention
A short cognitive check on the phone. Which check ran, how many trials and whether it was completed are recorded in the proof.
What your auditor sees
A STANDARD APPROVAL LOG
user:   admin
action: deploy v2.4.1
status: approved
A script can write these three lines. Nothing shows that a person was there, or what they read.
A GATEGUARD PROOF
Every line can be checked offline against published keys, years later, without calling us.
How it works
01
Request
Your system makes one API call with the action and the exact sentence the approver must read. You get a link back and send it to that person.
02
Authenticate
The person reads the sentence on their phone and approves or denies with their passkey. A request can be decided only once.
03
Cognitive check
Fifteen quick colour trials, or a reflex round first for sensitive actions. The stimuli are drawn on the screen, not written into the page.
04
Seal
The decision is signed and sent to you by webhook or API. Keep the proof with the action it authorised, and verify it whenever you need to.
What a proof establishes
A small signed document. Anyone holding it can check it against our published public keys, without calling us.
The decision and the moment
Approved or denied, with the time it was issued.
The human factor
Passkey verified on the device. A passkey that syncs through a cloud account is flagged as such.
Presence
Which check ran, how many trials, whether it was completed, and whether the signals can be trusted.
Two signatures
ES256 today, and ML-DSA-65 for the day quantum computers matter.
A timestamp no one can rewrite
The batch containing the proof is anchored in Bitcoin, with an inclusion proof you can check yourself. A proof cannot be backdated.
Calibration before scoring
The cognitive check is measured and recorded on every approval. A presence score is published only once the model is calibrated on labelled data, so that a proof never carries a number we cannot defend. Until then each proof states it: calibrated is false, band is unrated.
{
  "v": 2,
  "proof_id": "ggp_01M77V6H36NK...",
  "action": "agent.deploy",
  "decision": "approved",
  "display_sha256": "05353e2d1767...",
  "human_factor": {
    "method": "webauthn",
    "user_verified": true
  },
  "issued_at": "2026-11-12T12:19:54Z",
  "presence": {
    "model": "presence-v1",
    "calibrated": false,
    "band": "unrated",
    "challenge": {
      "kind": "stroop",
      "trials": 15,
      "completed": true,
      "level": "standard"
    },
    "signals": "trusted",
    "flags": ["synced_passkey"]
  },
  "sig": {
    "es256":   { "kid": "e6IaEt7...", "value": "0wLNUMH..." },
    "mldsa65": { "kid": "stpTaIm...", "value": "R5JYfSA..." }
  }
}
Shortened from a real proof issued on 12 November 2026.
Built for
AI agents
A human gate before an agent deploys to production, spends money or deletes data. The approval is tied to one action, not to a session.
Finance
Transfers, refunds and beneficiary changes. The amount and the beneficiary are in the sentence the approver read.
Security operations
Privileged access, production changes, alarm overrides. Each one leaves a proof that stands on its own in an audit.
Designed to be checked
Keys in hardware
The signing key lives in an Azure hardware security module and cannot be exported.
Offline verification
Public keys are published. A proof can be verified without any call to GateGuard.
Anchored in Bitcoin
Proofs are grouped in batches and timestamped on the Bitcoin blockchain through OpenTimestamps. A proof cannot be backdated.
Little data, by design
No photo, no voice, no biometric image. IP addresses are never stored in clear.
Patent pending
The underlying technology is covered by several patent applications filed with INPI, the French patent office.